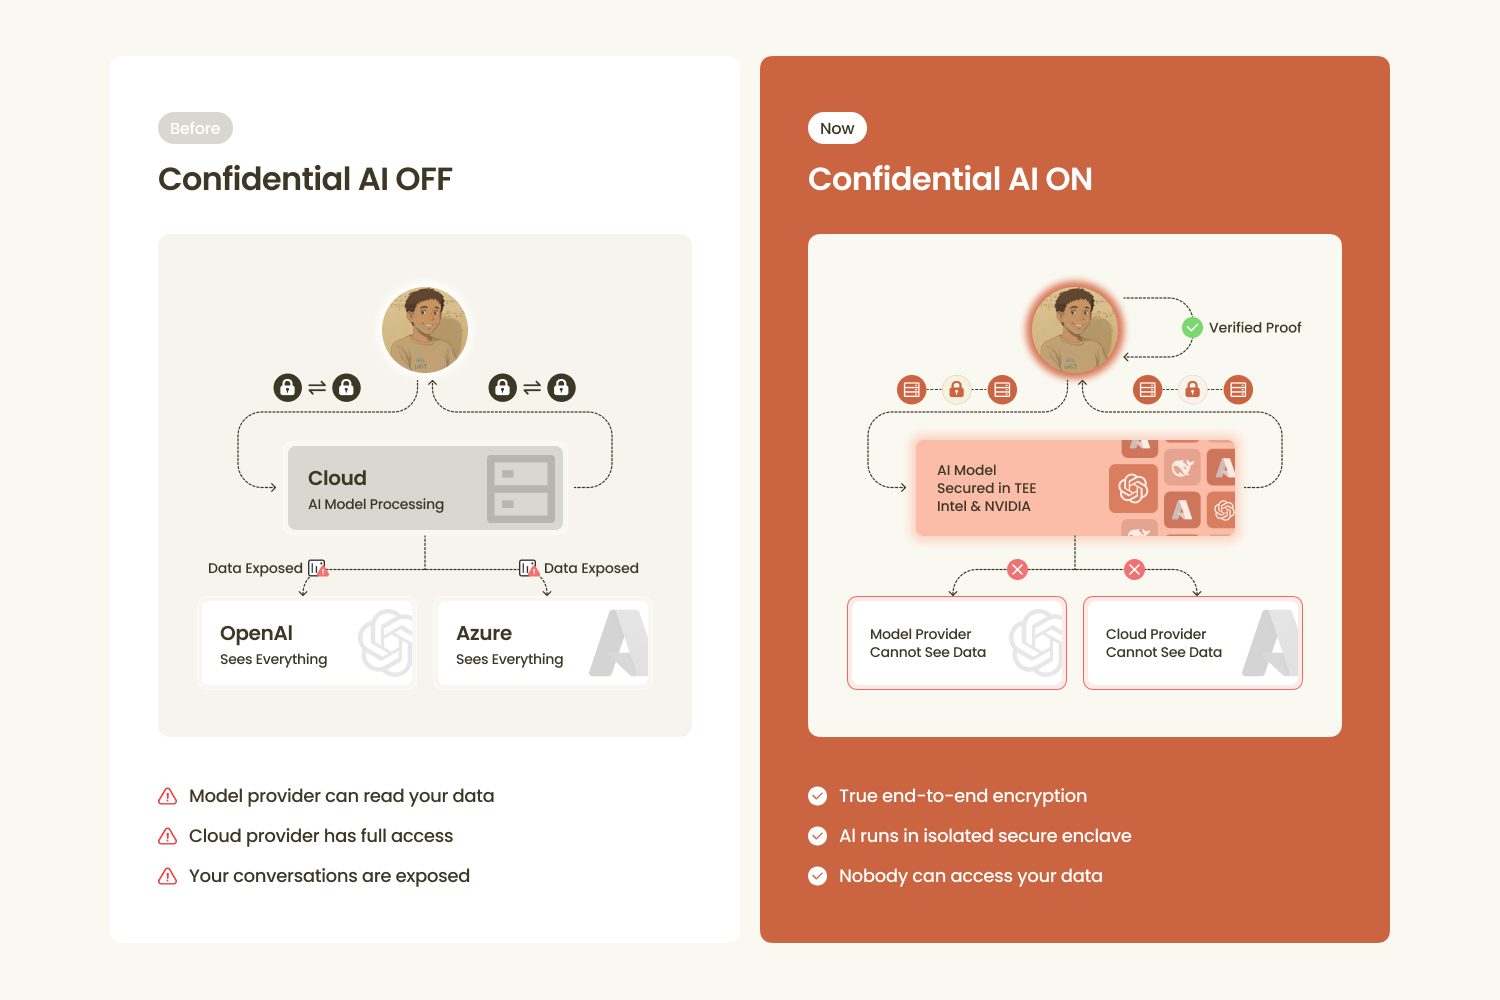
Confidential AI RedPill is an OpenAI-compatible inference API served by a gateway that runs inside a Trusted Execution Environment (TEE). Every response comes with evidence you can verify: an attestation report identifying the measured workload, and a signed receipt binding your request and response to it. Confidential models go further and run on a verified upstream enclave, with the channel bound before your prompt is forwarded.

How do you want to use RedPill?

Build with the API

Point your OpenAI or Anthropic SDK at one endpoint. Confidential and standard models, with a signed receipt on every response.

Use RedPill in an agent

Run Claude Code, Codex, Pi, OpenCode, and more through Private AI Proxy, a desktop app that verifies the gateway and connects your agents.

Use the chat app

End-to-end encrypted chat with confidential models and private document knowledge bases.

Onboard your agent

Give an agent RedPill guidance and one account-management interface without changing the current project or its model provider. The button copies the same canonical prompt used on redpill.ai. The agent installs the RedPill skill and uses Account MCP when the host supports remote MCP servers. Hosts with only a shell use the RedPill CLI instead. Use one account interface on a given host, not both.

Verify, don’t trust

After one request you can check, locally, that the gateway is a measured workload running in a genuine TEE, and that the response came from that workload unaltered and, for a confidential model, ran on a verified upstream enclave. How confidential AI works explains the model; Verify a response runs the checks.